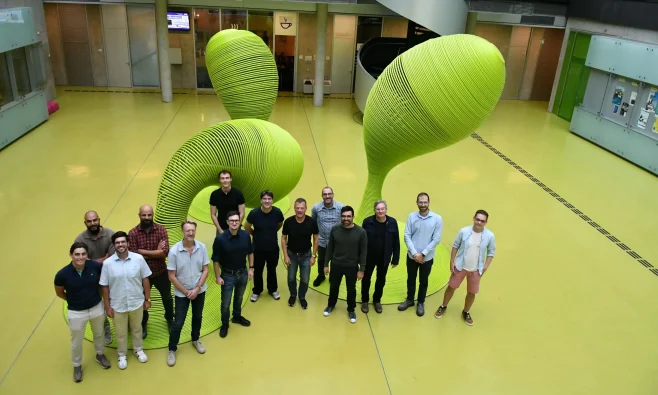
Second CHORYS General Assembly at TU Dresden: progress, EU review and Cyso's role
CHORYS met at TU Dresden. What EU reviewers said about this RISC-V cloud project, and Cyso's role.

Martijn Wokke
October 6th, 2026 · 4 min
At Cyso, trust forms the foundation of every service we deliver. Our Trust Centre provides complete visibility into our security practices, compliance certifications, and data protection measures.
Our commitment to security, compliance, and technical excellence is validated through rigorous third-party certifications. These industry-recognised standards demonstrate our systematic approach to protecting your data, maintaining service quality, and delivering enterprise-grade cloud infrastructure that meets the most demanding regulatory requirements.
The ISO/IEC 27001 sets the requirements for running an information security management system. Under this framework, security, risk management, incident response, change control and capacity planning all get handled systematically and stay auditable. Cyso works under a standard SLA that spells out what you get: response times, availability guarantees, monitoring and recovery procedures.
The NEN 7510 standard is the Dutch information security standard for healthcare, built on top of ISO 27001. It adds the healthcare-specific pieces: privacy protection, access to patient information, data handling and logging every action in electronic health records. With our NEN 7510 certification, your organisation meets those healthcare security standards.
Cyso holds Kubernetes Certified Service Provider (KCSP) status, a recognition the Cloud Native Computing Foundation (CNCF) gives to organisations with proven Kubernetes expertise. It confirms our engineers know container orchestration in practice, from enterprise deployment strategies to troubleshooting complex environments.
A SOC 2 Type II report confirms that a service organisation handles outsourced IT processes securely, not just on paper but effectively in day-to-day practice. An independent auditor verifies that every security control has worked consistently across a period of at least six months. It's proof the safeguards hold up over time.
Dutch Cloud Community Membership
As a member of the Dutch Cloud Community, Cyso Cloud actively supports the Netherlands’ digital sovereignty and cloud sector development. The DCC represents over 110 Dutch hosting and cloud providers, advocating for fair procurement processes and promoting European alternatives to global hyperscalers.
Cloud Native Computing Foundation (CNCF) Membership
Through our CNCF membership, Cyso Cloud participates in the global community advancing cloud-native technologies. This membership validates our technical expertise through our Kubernetes Certified Service Provider status. Our CNCF participation enables us to contribute to the democratisation of modern cloud technologies for European organisations.
Linux Foundation Europe Membership
As a member of the Linux Foundation Europe, Cyso Cloud is part of the European chapter of the world’s leading organisation for open source collaboration and innovation. Linux Foundation Europe drives open source adoption and digital sovereignty across the continent, supporting projects and organisations that keep critical technology infrastructure open, transparent, and independent. Our membership reflects our commitment to open standards and vendor-neutral technology.

Service Level Agreements
Our standard SLA guarantees 99.99% uptime with clearly defined response times, escalation procedures, and compensation frameworks. Comprehensive monitoring systems provide real-time service status visibility.
Disaster Recovery & Failover
Multi-zone architecture provides automatic failover capabilities with geographically distributed backup systems. Recovery time objectives (RTO) and recovery point objectives (RPO) are clearly defined and regularly tested.
Incident Response & Support
24/7 security operations centre with dedicated incident response team. Comprehensive incident management procedures include communication protocols, remediation processes, and post-incident analysis.
Security forms the foundation of everything we build. Our multi-layered approach combines physical data centre protection with advanced network defences and strict access controls. Every component of our infrastructure is designed to protect your data, applications, and business operations whilst maintaining complete compliance with European regulations.
Your data remains your property at all times. We operate exclusively within Europe from our datacenters in Amsterdam and Frankfurt, protected by European privacy laws including GDPR compliance. Our infrastructure maintains complete data sovereignty with no unauthorised transfers outside the EU.
Our entire network infrastructure features automatic DDoS protection with detection and mitigation systems. All instances are secured with asymmetric cryptography and Secure Shell access by default. Security Groups function as virtual firewalls, providing granular network access control.
Two-factor authentication (2FA) is mandatory for all account access. Our access control systems operate on role-based principles with comprehensive logging and audit trails. All personnel with system access undergo thorough security screening and background checks.
All mission-critical platform components feature redundant architecture (N+1) across multiple availability zones. Data storage includes redundant backup systems (N+2) with geographically distributed recovery options. Our data centres meet stringent physical security requirements including multi-layered access controls.
Do you have any questions about our policies or services? Make sure to get in touch with us and schedule a call today.
Discover best practices for GDPR-compliant deployments, learn about the latest Open Source innovations, and explore real-world case studies from organizations successfully navigating their digital transformation journey.
CHORYS met at TU Dresden. What EU reviewers said about this RISC-V cloud project, and Cyso's role.
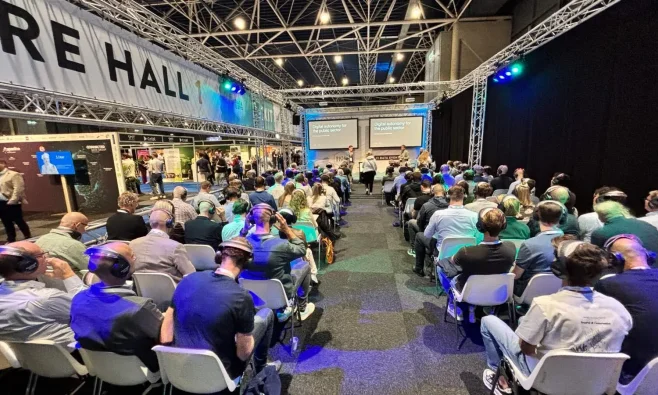
On Wednesday 9 September, the room at Data Expo 2026 was full for the talk: Digital autonomy for the public sector: not a big bang, but a realistic path.
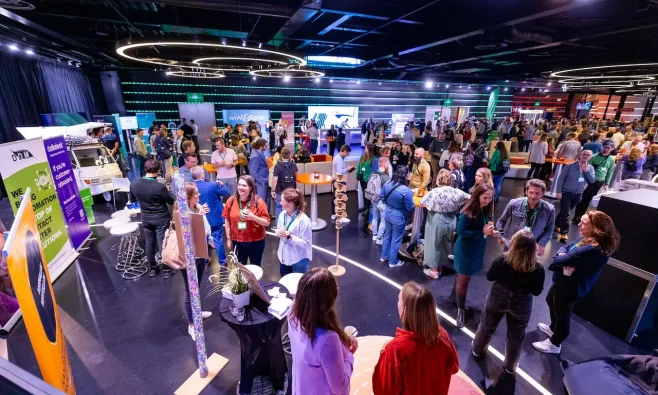
Cyso sponsors Dutch Cloud Native Day 2026. Talk Kubernetes, platform engineering and sovereign AI infrastructure at our booth, 29–30 Oct in Utrecht.
